
Introduction
Modern enterprises use encryption across almost every layer of their digital infrastructure.
Businesses encrypt databases, cloud storage, application information, backups, communications, and other sensitive data.
Every encryption process depends on cryptographic keys.
As organizations expand their infrastructure, they can accumulate large numbers of keys across different systems.
Managing these keys independently can create operational and security challenges.
Security teams may struggle to determine which keys exist, who owns them, what information they protect, and when they should be rotated.
Centralized Key management provides a way to address these challenges.
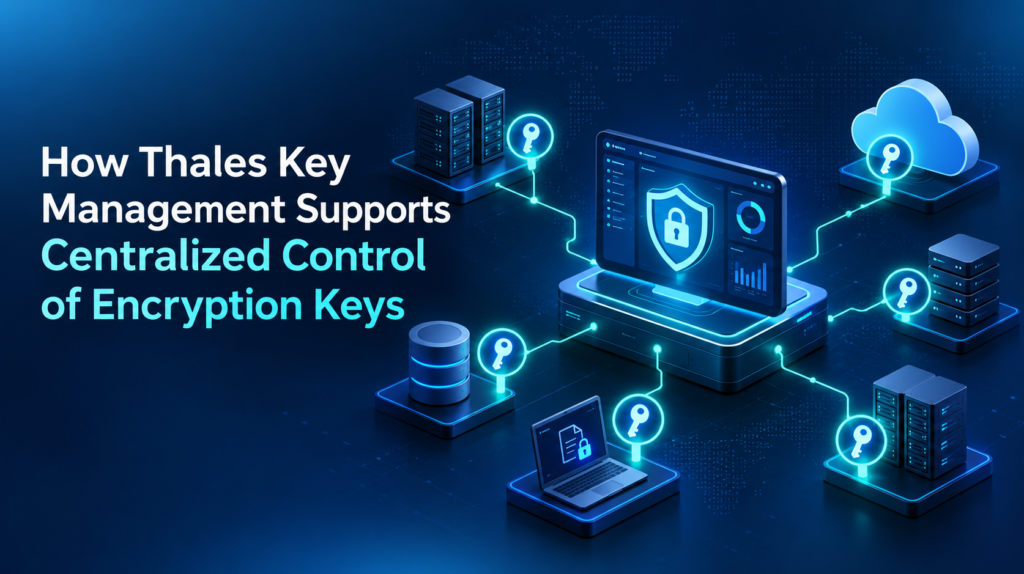
Thales key management can support organizations that need centralized capabilities for managing encryption keys across distributed enterprise environments.
Why Centralized Key Management Matters
Organizations often operate multiple technology environments.
These may include:
- On-premises data centers
- Public cloud platforms
- Private clouds
- Hybrid infrastructure
- SaaS applications
- Enterprise databases
Each environment may use different encryption mechanisms.
Without centralized management, teams may apply different policies to different systems.
This can create inconsistent security controls.
Understanding Key Management in Cryptography
Key management in cryptography covers the processes used to control cryptographic keys throughout their lifecycle.
The lifecycle typically includes:
- Generation
- Storage
- Distribution
- Access
- Usage
- Rotation
- Backup
- Recovery
- Retirement
- Destruction
Centralized Key management can help organizations coordinate these processes.
Key Visibility
One of the most important advantages of centralized management involves visibility.
Security teams should know:
- How many keys exist
- Which systems use them
- What information they protect
- Who owns them
- When they expire or rotate
Centralized management can provide a more structured view of these assets.
Key Ownership
Every important cryptographic key should have clear ownership.
The owner should understand the purpose of the key and its lifecycle requirements.
Ownership can help organizations maintain accountability.
Access Management
Cryptographic keys require strict access controls.
Organizations should apply least-privilege principles.
A user or application should access only the keys required for its approved function.
Centralized Key management can help security teams define and enforce consistent access policies.
Key Rotation
Organizations should rotate cryptographic keys according to their security policies.
Centralized management can help security teams coordinate rotation across multiple systems.
Automation can also reduce manual errors.
However, organizations should test rotation procedures carefully before applying them to critical production systems.
Key Backup and Recovery
Organizations need secure key recovery processes.
If a critical encryption key becomes unavailable, authorized applications may lose access to encrypted information.
Centralized Key management can help businesses establish documented backup and recovery processes.
Organizations should regularly test recovery procedures.
Key Retirement
Organizations should retire keys when they no longer serve an active purpose.
Leaving obsolete keys active can create unnecessary exposure.
Centralized management can help security teams identify keys associated with retired applications and systems.
Thales Key Management
Thales key management can support centralized control over encryption keys across distributed infrastructure.
Centralized management can help organizations maintain consistent policies for:
- Key lifecycle
- Key access
- Key rotation
- Key ownership
- Cryptographic activity
This approach can become particularly valuable when organizations operate across multiple infrastructure environments.
Cloud and Hybrid Infrastructure
Cloud and hybrid environments often increase Key management complexity.
An enterprise may store data in a cloud database while running applications on-premises.
Another application may operate on a different cloud platform.
The organization needs a consistent way to control the keys supporting these systems.
Centralized Key management can provide a common framework.
Supporting Application Security
Applications frequently use encryption to protect sensitive information.
Developers should avoid embedding sensitive cryptographic keys directly into source code.
Centralized Key management allows applications to request approved cryptographic access without requiring developers to manage keys manually.
Database Security
Organizations use encryption to protect sensitive database information.
The database may contain:
- Customer information
- Financial records
- Employee data
- Transaction records
- Business information
The corresponding encryption keys require protection.
Centralized Key management can help organizations control database encryption keys consistently.
Monitoring and Auditing
Centralized management can also support visibility into cryptographic activity.
Security teams should monitor:
- Key creation
- Key access
- Key rotation
- Administrative changes
- Failed access attempts
- Key retirement
These records can support security monitoring and investigations.
Benefits of Centralized Key Management
Improved Visibility
Organizations can maintain a clearer view of cryptographic assets.
Consistent Policies
Security teams can apply common lifecycle and access policies.
Better Governance
Centralized records can support security reviews.
Reduced Administrative Complexity
Teams can manage cryptographic assets using structured processes.
Improved Lifecycle Control
Organizations can coordinate key generation, rotation, and retirement.
Best Practices
Businesses should:
- Maintain a complete key inventory
- Assign key ownership
- Apply least privilege
- Separate keys from data
- Automate appropriate lifecycle processes
- Monitor cryptographic activity
- Test recovery procedures
- Retire obsolete keys
Conclusion
Organizations need strong control over encryption keys as their digital environments become more distributed.
Thales key management can support centralized administration of encryption keys across enterprise environments.
Key management in cryptography provides the lifecycle framework for generating, storing, using, rotating, recovering, and retiring cryptographic keys.
Effective Key management can improve visibility, access control, governance, and operational consistency.
By adopting centralized management and integrating it into their wider cybersecurity architecture, enterprises can establish stronger control over the cryptographic keys that protect critical business information.